EU E-Invoicing & Tax Reporting Knowledge Base

Product guides and frameworks for EU e-invoicing, Peppol, EN 16931, VAT reporting, tax authority integrations and rollout readiness.

SAF-T vs CTC vs E-Invoicing: How They Fit Together

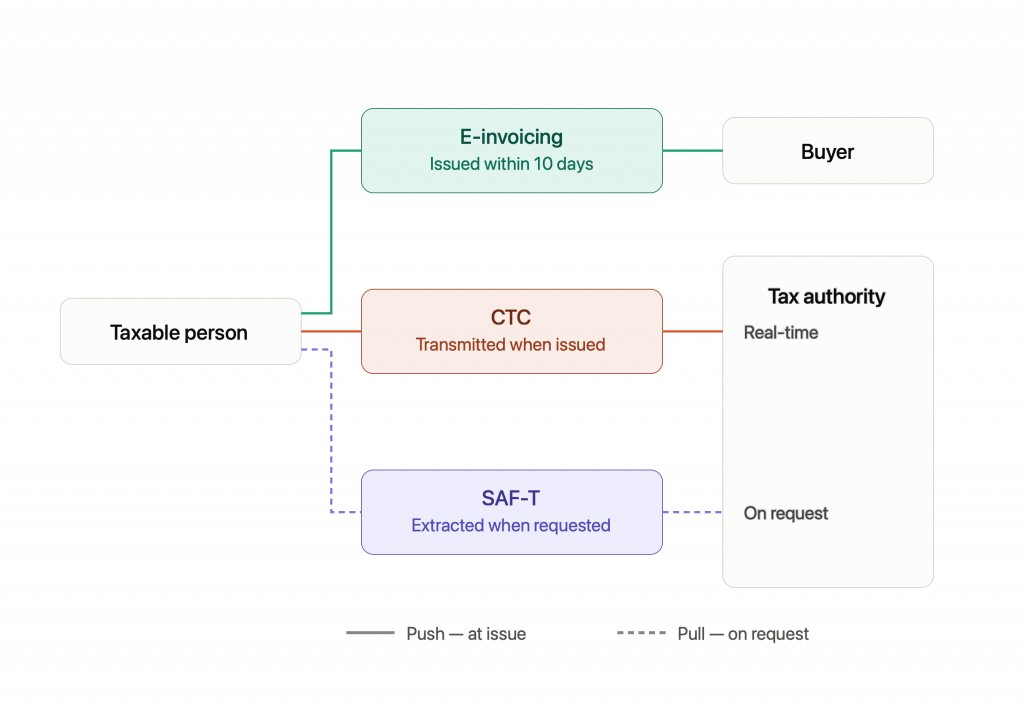
They are not three stages of one evolution. They are three different objects. E-invoicing carries the document you sent to your buyer. CTC transmits the transaction you issued, at the moment you issued it. SAF-T exports what you booked — the general ledger, the master files, the whole accounting record — either when the tax authority asks, or on a monthly cycle.

Those three things can disagree with each other. That is the entire reason a tax administration wants all three. And it’s why ViDA — which people keep describing as the end of periodic reporting — explicitly preserves SAF-T in the same breath as it mandates real-time transmission.

The map: what distinguishes them is the source object

Most explanations sort these by speed, which is why they end up confusing. Sort them by what the data is extracted from and the model resolves.
j

  • E-invoicing — source object: the invoice document. Recipient: the buyer. Governed by Directive 2014/55/EU and EN 16931. Deadline under ViDA: ten days from the chargeable event (Article 222). Integrity model: schema plus Schematron validation.
  • CTC — source object: the transaction as invoiced. Recipient: the tax authority. Governed by Chapter 6 of the VAT Directive as replaced by ViDA. Deadline: the moment the invoice is issued (Article 263(1)). Integrity model: cross-checking your report against your counterparty’s.
  • SAF-T — source object: the accounting record. Recipient: the tax authority or an auditor. Governed by national law, built on an OECD template. Deadline: on request, or periodically. Integrity model: referential integrity across the file.

Different objects, different owners inside your business. The invoice belongs to billing. The CTC report belongs to tax. The SAF-T file belongs to finance and the chart of accounts. A project that treats them as one integration will discover this the hard way.

SAF-T: the ledger, on request

The OECD’s Committee on Fiscal Affairs published SAF-T version 1.0 in May 2005, built around entries from a General Ledger Chart of Accounts together with master file data for customers and suppliers, and details of invoices, orders, payments and adjustments. Version 2.0, published in 2010, added inventory and fixed assets, and moved the schema from DTD to XML Schema — not fully backward compatible with 1.0.

Read the OECD’s own statement of purpose and the difference from CTC is immediate: SAF-T exists so that errors can be identified and quantified efficiently in the initial stages of an audit, letting auditors target resources at errors with material impact. It is audit tooling. The guidance even frames self-audit as a benefit — businesses reviewing their own transactions and adjusting before a return is filed. Nothing about that is real-time, and nothing about it is transactional control.

Two design details matter for anyone building to it. First, constraints are a deliberate feature: where a customer reference appears at transaction level, there must be a corresponding entry in the customer master file. SAF-T’s integrity model is referential integrity across the whole extract — a fundamentally different test from “does this invoice validate”. Second, the schema includes deliberate extension points, and the OECD is explicit that adding elements anywhere else makes the file incompatible with the OECD model. That is the same narrow-and-widen pattern EN 16931 uses with CIUS and Extensions, arrived at independently.

In practice there is no harmonised European SAF-T. Portugal went first in 2008 — mandatory for large firms using computerised accounting from 2009, extended to all VAT-registered entities by 2013 — and SAF-T (PT) integrates with the e-fatura system. Austria implemented it in 2009 on an on-demand basis. Luxembourg’s FAIA followed in 2011, on request, with penalties reported at up to EUR 5,000 per infraction or EUR 50–1,000 daily. Norway serves it on demand through Altinn. France uses FEC, its own SAF-T-inspired format, entirely separate from the OECD schema. Each country adapts, and the extension points are why they can.

CTC: the transaction, as it happens

Continuous transaction controls invert SAF-T’s direction. Instead of the authority reserving a right to come and look, the data arrives on its own.

Under ViDA, from 1 July 2030, an intra-EU B2B supply is transmitted per individual transaction at the moment the invoice is issued or should have been (Article 263(1)), carrying ten data points fixed identically across every member state (Article 264) — Article 226 points 1 to 4, 6, 7, 8, 11, 16 and 17, plus 11a where applicable. The customer reports within five days of receipt unless the member state waives it. Recapitulative statements are abolished outright: Articles 265 to 271 are deleted.

What CTC can see is exactly one thing: invoices, as issued. That is a narrow window, and it is the reason SAF-T survives.

E-invoicing: the exchange, which is neither of the above

E-invoicing is the only one of the three that isn’t a reporting obligation at all. It’s a private exchange between a supplier and a buyer, and its purpose is that the buyer can book and pay.

The historical proof sits in the Euro Retail Payments Board’s 2016 working group report, which categorises e-invoicing solutions by the number of intermediary platforms in the presentation flow: Supplier Direct, Buyer Direct, three-corner, four-corner. The tax authority is not a corner in any of them. In 2016 that wasn’t an omission — e-invoicing was defined as a two-party exchange, and the industry only invented a fifth corner once tax authorities arrived.

The dependency now runs the other way, and only one way. ViDA’s new Article 217 requires an invoice to be structured “at least in relation to the data referred to in Articles 262 and 271b” — the reporting articles. The reporting layer sets the structured floor for the exchange layer. Not your buyer’s needs. Not yours.

Why ViDA doesn’t kill SAF-T — and says so

This is the part the vendor explainers skip, and it’s decided in the directive’s own text.

ViDA’s recital 23 states that member states should be allowed to keep their national reporting tools — based, for example, on a SAF-T system — alongside the real-time obligations the directive introduces, together with non-general obligations such as those covering cash registers. It then draws the line explicitly: the ability of member states to request information from taxable persons during audits should not be limited, insofar as such information is obtained only at the member state’s request and does not result from active communication by taxpayers.

That sentence is the architecture. Pull versus push. Information the authority asks for is audit logic and stays permitted without limit. Information the taxpayer actively transmits is reporting logic and is now governed by Chapter 6. Article 273 carries it into the operative text: member states may not impose new general transaction-based reporting obligations on Article 262 transactions beyond Chapter 6 — but they may require taxable persons to keep transaction data for preparing the VAT return or for audit purposes, and they may impose reporting obligations for transactions outside Chapter 6’s scope.

So the boundary isn’t speed. It’s who initiates. And it means the practical answer to “does CTC replace SAF-T” is no: CTC takes the invoice-shaped transactions inside Chapter 6, and SAF-T keeps everything else — accruals, fixed assets, stock movements, bad debt relief, the credit note you never issued, the journal entry that reclassified a cost. CTC cannot see any of that, because none of it is an invoice.

Where the three collapse into one: Greece, Lithuania, Poland

The clean model above is a way to reason, not a description of what countries build. Three examples show the layers fusing.

Greece is the sharpest case, and SAP’s August 2024 implementation guide for Greek e-invoicing states it outright: myDATA accepts all revenue, expense and VAT-related documents from Greek businesses, thereby fulfilling the eBooks requirement — and the purpose of myDATA is the reconciliation of the accounting records of the liable entities with the tax authority’s e-books. That is a SAF-T objective. It is delivered over CTC plumbing (real-time submission through a certified service provider, with the platform returning a MARK, a UID and an authentication code) which itself rides on the e-invoicing exchange layer. All three layers, one message.

The tell is in the field list. The myDATA XML carries invoice type, total amount, net amount, VAT category — and then classification category and classification type. Those last two aren’t invoice fields at all; they’re accounting classifications, and SAP’s mapping derives them per document type from the G/L revenue or supplier offsetting account. A field in the invoice message whose value comes from the chart of accounts is the ledger layer bleeding into the transaction layer, in production.

Lithuania keeps them separate and names them. The i.MAS platform runs i.SAF for invoices, i.SAF-T for accounting data, and i.VAZ for goods transport — three modules, three source objects, one platform. The architecture in this article is not a theory; one member state shipped it as a product structure.

Poland runs both, and merged one of them with the VAT return. JPK arrived in July 2016 for large taxpayers and covered everyone by 2018. In 2020 JPK_VAT was replaced by JPK_V7M and JPK_V7K, which fold the VAT return and the underlying records into a single file — the return stopped being a separate document. Of the seven JPK structures, only JPK_V7M/K is submitted on a cycle, by the 25th; the rest, including the general ledger structure, are produced on request. And Poland mandates KSeF for e-invoicing on top. Two obligations, two layers, no overlap in the data.

The decisions, in the order you’ll face them

First: which layer does this requirement live on? If it names a document going to a counterparty, it’s exchange. If it names a transmission at the moment of issue, it’s CTC. If it names the general ledger, master files, or “on request”, it’s SAF-T. Requirements that name a G/L account inside an invoice message — Greece — are telling you the country has fused two layers, and your project scope just doubled.

Second: pull or push? Pull obligations are a data-availability problem: can you regenerate a consistent, referentially intact extract for a period that closed three years ago, after a chart-of-accounts migration? Push obligations are a latency and failure-handling problem: what happens at 14:59 when the endpoint is down and the invoice is issued at 15:00? These are not the same engineering problem and they rarely belong to the same team.

Third: assume they’ll be reconciled against each other. The reason to hold all three is that they’re derived from different objects and should agree. Greece says so explicitly — reconciliation of your accounting records against the authority’s copy. If your invoice data and your ledger data have never been reconciled internally, a tax authority is about to do it for you.

Frequently asked questions

Is SAF-T being replaced by CTC?

No. ViDA’s recital 23 explicitly permits member states to keep national reporting tools based on a SAF-T system alongside the directive’s real-time obligations, and Article 273 lets them require data retention for VAT return preparation and audit, and impose reporting on transactions outside Chapter 6. What Article 273 blocks is new general transaction-based reporting duplicating Chapter 6 for Article 262 transactions.

What’s the actual difference between SAF-T and CTC?

Source object and direction. SAF-T extracts the accounting record — general ledger, master files, fixed assets, inventory — and is typically produced on request. CTC transmits individual invoice transactions as they are issued. A CTC system can’t see a journal entry; a SAF-T file doesn’t arrive in real time.

Is e-invoicing a reporting obligation?

Not inherently. It’s an exchange between two businesses. Mandatory e-invoicing exists in countries with no tax authority controls at all, and in those cases nothing is reported to anyone. It becomes entangled with reporting only where a mandate connects the two — which, from 1 July 2030 for intra-EU supplies, ViDA does.

If a country has CTC, do I still need to file SAF-T?

Country by country, and frequently yes. Poland runs KSeF and JPK. Romania runs RO e-Invoice and the D406 SAF-T declaration. France is introducing mandatory e-invoicing while FEC remains a separate on-demand obligation. Budget for both unless the specific national law says otherwise.

Do the three ever carry the same data?

They overlap and none contains another. The invoice carries line items and delivery details the tax authority never receives. The ViDA report carries ten fields and not the parties’ names and addresses. SAF-T carries fixed assets and journal entries that never touched an invoice. Greece’s classification fields exist in the invoice message purely because myDATA is doing an accounting job through an invoicing channel.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base

E-Invoice Status Design: Submitted Is Not Accepted

An e-invoice has at least five statuses, and they are five different questions. Did the bytes arrive at the next hop? Did the document pass validation? Does the invoice legally exist? Does the counterparty agree with it? Can you prove any of this in ten years?

Most implementations collapse these into one field called status, and the collapse is where the defects live. A rejection arrives over a perfectly healthy connection. A delivery failure can be a terminal success. And the single most expensive state — “we don’t know” — usually isn’t modelled at all.

The five layers

Sorted by the question each one answers, not by the order they happen in.

  • Transport status — did the message reach the next hop? An HTTP code, an AS4 acknowledgement. Purely technical, and it says nothing whatsoever about the invoice.
  • Validation result — did it pass schema and business rules? Peppol’s MLR, Italy’s notifica di scarto, a JSON syntax error.
  • Legal status — does the invoice exist for VAT purposes? Greece’s MARK, India’s IRN, Italy’s ricevuta di consegna.
  • Counterparty acceptance — does the buyer agree? Peppol’s Invoice Response. This is a commercial axis, not a tax one.
  • Audit evidence — can you reconstruct the above years later? Signatures, authentication codes, retained receipts.

These are not stages of a pipeline. They’re orthogonal. You can be transport-successful and legally non-existent at the same time — that’s the normal case for a rejection.

A rejection is a successful transport

Italy’s Sistema di Interscambio is the clearest vocabulary anyone has built for this, because it names each state separately and attaches different legal consequences to each.

Submit a FatturaPA file and the SdI runs its checks, then returns one of several notifications. A notifica di scarto (NS) is a rejection with a numeric error code — and a rejected invoice is legally treated as never issued. The sender has five days to correct and resubmit, reusing the same invoice number and date to avoid penalties. A ricevuta di consegna (RC) means the invoice is both issued and delivered. And a mancata consegna (MC) means the recipient’s channel was unreachable: the SdI parks the invoice in the buyer’s reserved area on the Agenzia delle Entrate portal, and the invoice is still legally issued — delivery failure doesn’t invalidate it for VAT — but the sender must retain the MC notification as proof and tell the customer.

Read those three again as state transitions:

  • NS — transport succeeded, invoice does not exist.
  • RC — transport succeeded, invoice exists, buyer has it.
  • MC — transport succeeded, invoice exists, buyer does not have it, and this is a terminal success with an obligation attached rather than an error to retry.

All three arrive over the same healthy connection. A system whose status field is set from the HTTP response cannot distinguish any of them. And MC is the one that breaks naive designs: it looks like a failure, it is not a failure, and retrying it is wrong.

Peppol splits the same problem across three message types. The AS4 transport acknowledgement confirms gateway-to-gateway delivery and nothing more. The Message Level Response (MLR) reports the validation outcome, with codes like AP for accepted and RE for rejected. The Invoice Response — the business-level response — carries the buyer’s commercial decision: accepted, rejected, or under query. Three layers, three documents, and the industry considered the gap between them serious enough that Peppol finalised Message Level Status (MLS) in May 2025 specifically because MLR adoption was low and end-to-end visibility after the gateway was largely opaque.

The state nobody models: unknown

The best artefact in this entire subject is buried in SAP Hellas’s August 2024 implementation guide for Greek e-invoicing, and it’s worth reading closely.

The guide introduces a table, zgrein_edogrinv, that carries both a STATUS field and an HTTP_CODE field. Two status columns, side by side, in one table — because they answer different questions. It then defines the print logic in three branches:

  • Success — http_code = 201. The invoice reached the tax authority and a MARK was assigned. Print the MARK, the UID, the authentication code and the QR code.
  • Transmission failure between issuer and service provider, or a business error, or a JSON syntax error — http_code is neither 408 nor 201. Print an offline QR code, generated on the fly during the legal printing process.
  • Transmission failure between service provider and the tax authority — same offline QR treatment, different printed message.

Three things are happening here, and each is a lesson.

408 is carved out deliberately. A request timeout is the one code that means we don’t know — the submission may have landed. It gets neither the success path nor the failure path. That’s the unknown state, explicitly handled, and it’s the state most homegrown integrations skip straight past into a retry loop that duplicates invoices.

Transport failure and JSON syntax error share a branch. A network outage (not your fault, the invoice is fine) and a malformed payload (your fault, the invoice is wrong) both fall into the same condition and produce the same printed outcome. That’s the conflation this article is about, in production, in a vendor’s official guide. The branch is correct for the immediate purpose — print something legal — and wrong for everything downstream, because one of those needs a retry and the other needs a code fix.

When nobody is reachable, you mint your own evidence. The offline QR exists because the invoice has to be printed regardless, for business reasons, when communication fails through network outage or application errors. The API endpoint that issues it is literally named TransmissionFailure. That is a fifth state — issued, unreported, evidence self-generated — and it has no equivalent in any status enum that runs from pending to sent to error.

The same guide contains the whole thesis in one configuration note: the status field can drive specific messages on the invoice printout if it is not SUBMITTED. Submitted is the happy path. Everything else has to say so, on paper, to a human.

Validation is not a property of the document

This one surprises people. SAP’s own documentation on Peppol message types notes that the sending and receiving access points may be checking against different versions of the Schematron rules — so a document can pass validation at the sender’s access point and fail at the receiver’s.

Validity, then, is a property of a document and a validator and a moment in time. Italy makes the same point on a schedule: FatturaPA v1.9.1 takes effect 15 May 2026 with new error codes, and a file that validated two years ago can fail today if your generator hasn’t tracked the specification. If you cache a boolean is_valid against an invoice, you have stored the answer to a question that has since changed.

Worse, absence of rejection is not acceptance. Peppol’s MLR is an optional document — not every sender supports receiving one, and the receiver has to query the SMP to find out whether the sender does. If your model treats “no negative response” as success, it will report success for every counterparty that never agreed to tell you.

Acceptance is a different axis entirely

Tax acceptance and commercial acceptance are unrelated, and conflating them produces the worst class of bug: a legally valid invoice marked as failed because the buyer disputed it, or an accepted invoice that never legally existed.

Peppol keeps them apart by design — an MLR rejection is a technical failure you fix with better validation, while an Invoice Response rejection is a business dispute that requires a conversation. Italy keeps them apart too, and asymmetrically: public administrations can refuse an invoice received through the SdI and the system carries a separate outcome notification plus a deadline notification for when the acceptance window expires. B2B buyers get no such right — once an invoice clears for VAT, the buyer cannot reject it, and the remedy is a credit note.

So “rejected” means at least three unrelated things depending on who said it. Model the speaker, not just the verdict.

Your state machine’s transitions are legislated

Here’s the constraint that catches product teams: the transitions are not yours to design.

SAP’s Greek guide describes a framework offering submission, cancellation, resubmission and deletion of e-documents, with deletion only available in the created status. Then it records that, following a Greek ministerial decision, the cancel function is no longer available at all — companies must issue credit notes as a substitute. A transition was removed from the state machine by law, after the software was built.

The same guide ships a configuration table, EDOMETASTATUSV, whose entire purpose is assigning eDocument process status to status. Roughly twenty process states — matched, match error, cancelled, created, deviation rejected, added to summary — collapse onto three status codes. The mapping table exists precisely because the process status and the status are not the same thing, and someone had to write down the relationship. Note also that the guide’s V3 revision renamed the old status field to http_status. Somebody hit this ambiguity and fixed it in the field name.

What to build

Separate fields, not one enum. At minimum: transport outcome, validation outcome, legal identifier (present or absent), counterparty response, and evidence reference. Greece ships two of these in one table already. Derive a display status from them; never store only the derived value.

Model unknown as a first-class state. Timeouts, not just successes and failures. An unknown submission needs a reconciliation query against the authority, not a retry — retrying an invoice that landed is how you create duplicates in a system where the sequential number is legally significant.

Make failure states carry their obligation. Italy’s MC requires retaining the notification and notifying the customer. Greece’s transmission failure requires printing an offline QR. Neither is “retry later”. If your error state has no field for the obligation it triggers, someone will do it manually or not at all.

Store the evidence, not a log line. Under ViDA, Article 138(1a) removes the exemption for an intra-Community supply where the supplier hasn’t met the transmission obligation or the data is wrong — unless the failure can be duly justified to the competent authorities. “Duly justified” is a data requirement. It means the artefact that proves you tried, retained for as long as the invoice itself: Italy requires ten years of electronic preservation, and audits check the receipts, rejections and resubmission logs alongside the invoices.

Frequently asked questions

What’s the difference between an MLR and an Invoice Response in Peppol?

An MLR is a technical response about validation — it tells you whether the document was structurally acceptable and processed, using codes such as AP and RE. An Invoice Response is a business-level document carrying the buyer’s commercial decision: accepted, rejected, or under query. An MLR rejection is fixed with better validation. An Invoice Response rejection is a dispute.

If I get an HTTP 200, is my invoice filed?

No. The transport succeeded; that’s all you know. In Italy the same successful connection can carry a notifica di scarto, which means the invoice is legally treated as never issued. In Greece, only http_code = 201 with a returned MARK means the tax authority holds it.

What should happen on a timeout?

Not a blind retry. A timeout is the unknown state — the submission may have been processed. Query the authority for the document’s status before resubmitting, because re-sending a landed invoice creates a duplicate against a sequential number that carries legal weight. Greece’s guide treats HTTP 408 as its own branch for exactly this reason.

Can a delivery failure be a success?

Yes. Italy’s mancata consegna means the invoice is legally issued but the buyer’s channel was unreachable, so it sits in their portal area. It doesn’t invalidate the invoice for VAT. It’s a terminal state with two obligations — retain the notification, inform the customer — not an error to retry.

How long do I need to keep the receipts?

As long as the invoices, and treat them as part of the same record. Italy requires ten years of compliant electronic preservation and audits verify the delivery receipts, rejection notifications and resubmission logs. Under ViDA, the ability to duly justify a transmission failure is what stands between you and losing an exemption — which is only possible if the evidence survived.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base

E-Invoice Corrections: Why You Can’t Just Cancel It

Once an invoice has cleared a tax authority, it is immutable. You cannot edit it. In most systems you cannot cancel it either, and where you can, the window is measured in hours and closing. What you get instead is a third verb: supersede. Issue a new document that points at the old one, and let the tax authority reconstruct the graph.

This is the part of e-invoicing that product teams model last and pay for first. The send is the easy bit — one document, one API call, one status. The lifecycle is a directed graph of documents that reference each other, some of which your counterparty creates, some of which lock others, and all of which are separately reportable.

Cancellation is a narrow exception, and it’s disappearing

India is the clearest illustration because its cancellation rule has a reason nobody expects. An e-invoice can be cancelled on the Invoice Registration Portal only within 24 hours of the IRN being generated — and the reason commonly given is that the IRP doesn’t store e-invoices for longer than that. The window on a legal operation is set by an infrastructure retention policy. After it closes, the portal simply blocks the option.

Three further constraints stack on top:

  • Amendment doesn’t exist at all. Once the IRN is generated the data is locked. Taxable value, tax rate, buyer details — none of it can be changed on the original. Changes are made when filing GSTR-1, and those get flagged to the officer, who may come back asking questions.
  • Partial cancellation is impossible. It’s the whole invoice or nothing.
  • A downstream document can veto it. If an e-way bill is active against the IRN, the IRP will not permit cancellation. The goods are moving; the invoice is pinned.

That last one is the shape of the whole problem. Your invoice is not a leaf node. Something else is holding a reference to it, and that reference removes an operation from your state machine.

Greece removes the operation differently, and SAP Hellas’s August 2024 implementation guide records it precisely: because the solution uses a service provider under the Greek YPAHES framework, the cancel function is no longer available, and companies must issue credit notes as a substitute for cancellations. Read the causation carefully — cancellation wasn’t banned outright, it was removed by the compliance route. The same SAP framework offers submission, cancellation, resubmission and deletion, with deletion only possible while the document is still in created status. Pick the service-provider path and one of those verbs quietly goes away.

Which means the available lifecycle operations are a function of the country and the architecture, not of your product. You do not get to decide whether your users can cancel.

Everything else is a new document pointing at the old one

The universal fallback is the credit note, and it’s worth being precise about what it is: not an edit, not a reversal flag, but a separate fiscal document with its own identity that references the original.

In India, once the 24 hours have passed, a credit note (for a reduction) or debit note (for an increase) referencing the original IRN is the only route — and that note must itself be e-invoiced where the supplier is inside the mandate threshold, generating its own IRN. The correction is recursive: fixing a reported document produces another reported document. In Italy, credit notes (TD04) and debit notes (TD05) go through the SdI referencing the original, on the same clearance path as the invoice itself.

ViDA then does something that makes this explicit in EU law. From 1 July 2030, Article 226 gains point 16: the sequential number of the corrected invoice, on a corrective invoice. The pointer becomes a mandatory legal field. And Article 264 puts point 16 inside the ten data points transmitted to the tax authority for a cross-border supply — so the edge of the graph is itself reported. The authority isn’t inferring the relationship from your reference field. It’s receiving it.

The simplified-invoice rule (Article 226b) has carried the same logic for years: a corrective document needs a specific and unambiguous reference to the initial invoice and to the specific details being amended. Note the second half. Not just “which invoice” — “what changed”.

What ViDA conspicuously does not add is a cancellation message. There is no “unsend” in the reporting model. Corrections are documents, and documents are all the authority sees.

Two countries, one question, opposite answers

Here’s the finding that should kill any attempt at a single global correction policy.

When Italy’s SdI rejects an invoice with a notifica di scarto, the invoice is legally treated as never issued, and the sender has five days to correct and resubmit — reusing the same invoice number and date to avoid penalties. The number must be reused, because as far as the law is concerned nothing was ever issued under it.

In India, after cancelling an IRN, you must not reuse the invoice number to generate a new one. The number is burned.

Same engineering question — is a document number reusable after a failed attempt? — and two mandates give opposite answers, both mandatory, both penalised. If your sequence generator has a global policy on reuse, it is wrong in at least one jurisdiction. This has to be per-country configuration, and it has to sit at the point where numbers are minted, which is usually the last place anyone wants country logic.

The graph has edges you don’t control

The lifecycle isn’t only yours to drive. Three examples, all live:

Your buyer can report you. Italy introduced document type TD29 in version 1.9 of the FatturaPA specification in April 2025, letting a buyer flag a supplier’s omitted or irregular invoice through the SdI — shifting part of the compliance responsibility onto the buyer. TD20 already allowed buyers to self-invoice omitted or irregular supplies. Your invoice’s lifecycle now has state transitions initiated by someone else’s finance team.

The counterparty’s clock is different from yours. In India, if an IRN is cancelled after the data has auto-populated into GSTR-1, the supplier amends GSTR-1 and the buyer’s GSTR-2B adjusts in the next cycle, generated on the 14th of the following month. The correction is instant on your side and up to a month late on theirs. Anything you build that assumes both parties see the same state at the same time is modelling a system that doesn’t exist.

Delivery failure creates obligations, not retries. Italy’s mancata consegna means the invoice is legally issued but the buyer’s channel was unreachable; the SdI parks it in their portal area, and the sender must retain the notification as proof and tell the customer. That’s a lifecycle branch whose next step is a phone call.

Payments and financing hang off the same document

The graph extends past tax. The Euro Retail Payments Board’s 2016 report defines a Request To Pay as a subset extracted from the invoice — the minimum needed to initiate payment, with a link back to the underlying invoice, and usually no tax detail or line items at all. That’s a fourth representation of the same transaction, with its own lifecycle, joined to the invoice by a reference.

Financing adds a fifth. OASIS built UBL as a general trade format aligned with ISO 20022 and designed to carry invoice financing, factoring and letters of credit. When an invoice is factored, a third party acquires a claim against a document that the tax authority may later treat as never having existed. The credit note that fixes your VAT position is also an event in somebody’s receivables book.

None of this is exotic. It’s the ordinary consequence of one document being referenced by several systems with different rules about what “cancelled” means.

What to model

Immutable documents, mutable graph. Never update a cleared invoice record. Append documents and edges. The tax authority’s view is a log, not a table — model yours the same way and reconciliation gets much easier.

Make the reference a first-class field, not a note. From 1 July 2030 the corrected invoice’s number is a legally mandated field that gets transmitted. Treat “which document does this supersede, and what changed” as structured data from the start; you’ll need both halves.

Model operations as per-country capabilities. Can this document be cancelled? For how long? Can the number be reused? Is a downstream document blocking it? Those are configuration, not code paths — India blocks cancellation with an active e-way bill, Greece removes cancel entirely on the service-provider route, Italy requires number reuse where India forbids it.

Assume corrections are recursive and reportable. A credit note against a reported invoice is itself a reported document with its own identifier and its own failure modes. If your reporting pipeline treats corrections as a special case outside the main flow, you have two pipelines and one of them is undertested.

Give the correction a reason, and keep it. Italy’s ravvedimento operoso lets businesses correct voluntarily and cut penalties substantially, but only where the correction is made before the authority opens a formal inspection — so the timestamp on your correction has money attached. Under ViDA, Article 138(1a) removes the exemption on an intra-Community supply where transmitted data is wrong, unless the failure can be duly justified. “Duly justified” is a field you either populated at the time or cannot reconstruct later.

Frequently asked questions

Can I edit an e-invoice after sending it?

No. In India the data is locked once the IRN is generated and amendment on the portal doesn’t exist. In clearance systems generally, the cleared document is the record; changes come through a new document that references it. Where a portal offers “amendment”, it usually means amending your return, not the invoice — and in India those amendments get flagged for the officer’s attention.

What’s the difference between cancelling and issuing a credit note?

Cancellation removes the invoice from existence, which is why it’s tightly time-boxed or unavailable. A credit note leaves the original standing and reverses its effect with a second document. India permits cancellation for 24 hours, then only credit notes. Greece, on the service-provider route, has no cancellation at all — credit notes substitute for it entirely.

Can I reuse the invoice number after a rejection?

It depends on the country, and the two big mandates disagree. Italy requires you to resubmit a rejected invoice with the same number and date within five days. India forbids reusing the number of a cancelled IRN. Make this configurable per jurisdiction.

Does a credit note need to be e-invoiced too?

Generally yes. In India a credit or debit note must itself be e-invoiced where the supplier is inside the mandate threshold, producing its own IRN. In Italy, TD04 credit notes and TD05 debit notes go through the SdI like any other document. Corrections are not a side channel.

Why can’t I cancel an invoice that has an e-way bill?

Because a downstream document is referencing it. India’s IRP refuses IRN cancellation while an e-way bill is active against it — the goods are in transit under that invoice, so the invoice can’t be unmade. It’s the clearest example of the general rule: your document’s available operations depend on what else in the graph points at it.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base

What Is an E-Invoicing Europe API?

Definition

An e-invoicing Europe API is an application programming interface that enables software products to create, validate, send, receive, track, and archive electronic invoices in European markets. It connects SaaS platforms, ERP systems, billing tools, marketplaces, or compliance products with e-invoicing networks, national platforms, tax authority systems, access points, and invoice validation services.

For product, compliance, and SaaS teams, an e-invoicing Europe API is not just a billing connector. It is a regulated data exchange layer that must handle invoice formats, routing, validation, submission status, audit evidence, country-specific rules, and changing regulatory requirements.

Why It Matters for Product Teams

E-invoicing in Europe is shaped by both EU-level standards and national mandates. The EU eInvoicing Directive required public authorities to be able to receive and process electronic invoices that comply with the European standard, with a final deadline in April 2020. The European standard EN 16931 defines the semantic data model for electronic invoices and supports interoperability across EU systems. (Internal Market & SMEs)

Product teams need to understand that “Europe” is not one implementation. E-invoicing workflows can differ by country, transaction type, buyer type, tax rules, network model, platform, and reporting obligation.

An e-invoicing Europe API can support:

  • invoice creation and validation
  • EN 16931 data mapping
  • Peppol routing
  • national platform submission
  • B2G and B2B invoice workflows
  • VAT reporting preparation
  • invoice status tracking
  • rejection handling
  • audit trails and archiving
  • customer-facing compliance evidence

The product risk is not only whether the API sends an invoice. The real question is whether the system can prove what was sent, when it was sent, whether it was accepted, why it failed, and what the customer should do next.

Common Implementation Questions

What should teams define first?

Start with the invoicing workflow. Identify the country, transaction type, customer type, invoice format, routing network, authority or platform, tax requirements, validation rules, evidence needs, and failure handling.

Is an e-invoicing Europe API the same as Peppol?

No. Peppol is an important e-document exchange network used for e-invoices and other business documents, but it is not the only model in Europe. Some countries use national platforms, clearance models, reporting systems, or specific local requirements. Peppol enables electronic exchange of e-invoices, purchase orders, and other business documents, but product teams still need to map the applicable country workflow.

What is EN 16931?

EN 16931 is the European standard for electronic invoicing. It defines a common semantic data model for electronic invoices, helping systems interpret invoice content consistently across different technical environments. Public entities covered by Directive 2014/55/EU must be able to receive and process invoices that comply with the European e-invoicing standard. (European Commission)

How does VAT in the Digital Age affect e-invoicing?

The EU adopted the VAT in the Digital Age package on 11 March 2025. It is expected to expand the role of e-invoicing and digital reporting across the EU over time, especially for cross-border VAT reporting. Product teams should monitor implementation timelines and national rollout plans instead of assuming one immediate EU-wide technical model.

What is the biggest implementation risk?

The biggest risk is treating European e-invoicing as a single API integration. In practice, teams may need to support multiple formats, validation rules, routing models, local mandates, authority responses, rejection codes, archiving requirements, and customer-specific workflows.

Can a vendor claim e-invoicing compliance?

Use caution. “Fully compliant” is risky unless the vendor defines the country, transaction type, standard, platform, legal role, data scope, evidence model, and date of assessment. Stronger wording explains what the API supports: EN 16931 mapping, invoice validation, Peppol routing, national platform integration, rejection handling, status tracking, archiving, and audit trails.

Related Standards and Frameworks

E-invoicing Europe API implementations often overlap with Directive 2014/55/EU, EN 16931, Peppol BIS Billing, national e-invoicing mandates, VAT reporting rules, tax authority specifications, data archiving requirements, GDPR, ISO/IEC 27001, API security controls, and ERP integration standards.

These frameworks do not create one universal European e-invoicing workflow. They help teams structure interoperability, validation, secure transmission, evidence, archiving, and country-specific compliance operations.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base

CRA Reporting Starts 11 September. Looking Starts in 2027

From 11 September 2026, a manufacturer that becomes aware of an actively exploited vulnerability in a product with digital elements has 24 hours to file an early warning with EU authorities. The obligation reaches backwards: it covers products already on the market, including ones shipped years ago and no longer under active development.

The obligation to have a vulnerability-handling process does not start until 11 December 2027. For fifteen months, manufacturers are legally required to report what they are not yet legally required to be looking for.

What the September obligation actually is

The Cyber Resilience Act, Regulation (EU) 2024/2847, entered into force on 10 December 2024. Its main obligations apply from 11 December 2027, which is the date most planning has been built around. Article 14 runs on a separate clock, and that clock starts first.

Two things trigger it: an actively exploited vulnerability contained in the product, and a severe incident having an impact on the product’s security. The timeline is staged — an early warning within 24 hours of becoming aware, a full notification within 72 hours, and a final report no later than 14 days after a corrective measure is available for an exploited vulnerability, or within a month for a severe incident.

“Actively exploited” is narrower than it sounds. It means evidence of real attacks against the product, not theoretical exploitability. A proof of concept or a research finding does not start the clock.

What “aware” means is the operationally difficult part. The Commission’s March 2026 draft guidance set the threshold at a reasonable degree of certainty that a vulnerability is being actively exploited or that a severe incident has compromised the product’s security. In practice that certainty often arrives only after an initial assessment, and manufacturers may hold off notifying until that assessment is complete. An ongoing investigation aimed at full forensic confirmation, however, is in principle no defence for missing the deadline.

Reports go in once, through the CRA Single Reporting Platform that ENISA is required to establish under Article 16. The notification is addressed to the CSIRT designated as coordinator where the manufacturer has its main establishment, and — absent particularly exceptional circumstances — reaches ENISA at the same time. That CSIRT then passes it to CSIRTs in every member state where the product has been made available.

The part that catches people

Article 69(3) is the provision to read before planning around December 2027. It applies Article 14 to products with digital elements that were placed on the EU market before 11 December 2027. A product shipped in 2015 and still on the market is in scope for reporting from September, regardless of what it predates.

Set that against the timing of everything else, and the shape of the gap becomes clear:

  • Reporting duty: 11 September 2026, covering the installed base.
  • Vulnerability-handling requirements in Annex I: not legally binding until 11 December 2027.
  • Essential cybersecurity requirements and conformity assessment: also 11 December 2027.

The practical consequence is that a manufacturer’s September exposure is determined by how quickly it learns things, not by how compliant its products are. Nothing in the Act obliges you to run threat intelligence, monitor exploitation of your own installed base, or maintain intake for third-party reports until the end of 2027. But once something reaches you through any route — a customer, a researcher, a vendor advisory, a news report — the 24-hour clock is running.

One more asymmetry worth noting: where the actively exploited vulnerability sits in an integrated component rather than the manufacturer’s own code, the obligation to notify still falls on the manufacturer of the product.

Whether the reporting channel itself is safe: an argument that has not been settled

The design requires manufacturers to hand governments detailed information about vulnerabilities that are being exploited and, by definition, may not yet be fixed. That has been contested since the legislative stage, and the disagreement is worth understanding on its own terms rather than as a settled question.

The objection during the negotiations, raised by the Electronic Frontier Foundation among others, was directed at what was then Article 11 of the proposal. EFF’s concern was that a reporting duty of this kind raises the risk of a vulnerability being “added to the offensive arsenal of government intelligence agencies.” A separate open letter from security researchers made a related argument: that dozens of agencies holding a live register of unmitigated vulnerabilities creates both a surveillance risk and an attractive target, and urged that only vulnerabilities with available mitigations be reportable.

The final regulation answers part of this through Article 16(2), which lets a manufacturer flag one of three narrow conditions in its 72-hour notification: that exploitation is confined to the member state of its own CSIRT, that wider dissemination would run against that state’s essential interests, or that dissemination poses an imminent high cybersecurity risk. Where a condition is flagged, ENISA initially receives only limited information — that a notification exists, general detail about the product, the general nature of the exploit — until the CSIRT releases the full text. A CSIRT may also delay dissemination where a coordinated vulnerability disclosure procedure is under way. On 11 December 2025 the Commission adopted a delegated act specifying the terms and conditions for applying those cybersecurity-related grounds.

Two points survive that machinery. The first is structural: flagging sensitivity limits who sees the content, but nothing pauses the filing itself. The 24-hour, 72-hour and final-report windows all run from awareness, and the decision to hold back dissemination belongs to the receiving CSIRT, not to the manufacturer.

The second came from the Cybersecurity Coalition and the Hacking Policy Council in their comments on the draft delegated act. Their argument is that the act addresses risk in sharing between CSIRTs but not in the leg before it — between manufacturer and CSIRT. They point to a specific case: a CSIRT may delay reporting via the Single Reporting Platform where the platform has itself been compromised, yet manufacturers are still required to submit through that same platform, and nothing requires ENISA to tell them about such an incident. On their reading, “manufacturers could unknowingly report vulnerabilities through a compromised or insecure channel.”

Reading the delegated act does not dissolve the disagreement. The Commission’s position is that Article 16 and the delegated act provide proportionate safeguards; the industry groups’ position is that the safeguards sit one link further down the chain than the risk. Both readings are available on the text. If your reporting process depends on how this resolves — because you ship security products, or operate in a sector where an unpatched-vulnerability disclosure carries second-order risk — this is a question for security counsel, not for a checklist.

Scope guidance arrived seven weeks before the deadline

Article 26 obliges the Commission to publish guidance helping economic operators apply the CRA, with particular attention to smaller businesses. It approved that guidance on 27 July 2026, document reference C(2026) 5252 — roughly 80 pages, with worked examples and flowcharts, following a consultation draft issued on 3 March 2026. It is not legally binding, but it is the reading that market surveillance authorities and notified bodies will work from.

Most of it addresses scope, which is where the genuine uncertainty has been. For free and open-source software, the guidance confirms that software published without being placed on the market generally falls outside the CRA. Where the publisher is a legal person meeting the definition of an open-source software steward under Article 3(14), only the obligations in Article 24 apply, with steward reporting duties calibrated to the support actually provided.

The line the guidance draws around commercial activity is the operative one. Selling the software, offering a paid enterprise edition, monetising services through it, requiring personal data beyond security or interoperability purposes, or making donations effectively mandatory for access or essential updates all bring a project into scope. Voluntary donations, sponsorships, public funding, and paid consulting, training or support do not, provided the software itself stays freely available. A contributor submitting patches or fixing bugs generally carries no CRA responsibility; obligations attach to whoever controls releases, roadmap and governance. An organisation publishing both a free community edition and a paid enterprise edition is steward of the first and manufacturer of the second — two regimes, same codebase.

If you are not established in the EU

Article 14 sets a sequence for determining which CSIRT receives the notification when the manufacturer has no main establishment in the Union: the authorised representative, then the importer, then the distributor, then the location of users. Working out that answer at the moment a 24-hour clock starts is the wrong time to do it. It is a question to settle in advance and write into the incident procedure, alongside who inside the organisation is authorised to decide that the awareness threshold has been met.

Frequently asked questions

Do I need a full vulnerability-handling process by 11 September 2026?

Not as a legal matter. The vulnerability-handling requirements in Annex I are not binding until 11 December 2027. From September 2026 the only obligation is to report actively exploited vulnerabilities and severe incidents. In practice the two are hard to separate — you cannot report reliably what no process is built to detect — but the deadlines are distinct and require different preparation.

Does this apply to products I shipped before the CRA existed?

Yes. Article 69(3) extends the Article 14 reporting obligations to in-scope products placed on the EU market before 11 December 2027. Age of the product is not a defence, and the practical work is inventorying what you still have on the market.

Can I delay reporting while I investigate?

Only up to a point. The clock starts at a reasonable degree of certainty, and the Commission’s guidance accepts that certainty may require an initial assessment. Continuing to investigate toward full forensic confirmation is in principle not a defence for missing the window. Separately, flagging sensitivity under Article 16(2) limits who sees the content — it does not pause the filing.

Does my open-source project fall under the CRA?

It depends on whether it is placed on the market in the course of a commercial activity. Free availability with voluntary donations, sponsorship or public funding generally stays outside scope; paid editions, monetised services, or donations that are effectively required for access bring it in. The Commission’s July 2026 guidance works through the borderline cases in detail and is the right document to check a specific project against.

What happens if I miss a deadline?

Enforcement sits with national market surveillance authorities, and the CRA’s enforcement model runs primarily through corrective measures rather than immediate financial penalties. That is a weaker deterrent than the AI Act’s or the GDPR’s, and it is also a reason not to treat September as soft: a corrective-measures process aimed at your product line is disruptive in ways a fine is not.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base

A TikToker tested a tax system with a fake condom invoice: it has no questions. And only a pharmacist saved the Polish PM’s office — and it’s clean tax record

KSeF Scam Invoices: The PM’s Office Didn’t Buy Condoms

In February 2026, a man walked into a pharmacy in a Polish shopping centre, bought a packet of condoms, and asked for the VAT invoice to be made out to the Chancellery of the Prime Minister. He gave the Chancellery’s tax number. He had no connection to it — no contract, no order, no relationship of any kind. Under rules that had taken effect two weeks earlier, none of that mattered. Had the pharmacist completed the request, the invoice would have been validated by the state and deposited in the Chancellery’s own records, and nobody working there could have refused it.

That is not a loophole. Poland’s Krajowy System e-Faktur routes every structured invoice to whoever’s tax identification number appears on it, and the workflow contains no step at which the recipient accepts or declines. Documents sent this way on purpose have earned a name in Polish practice: faktury scamowe, KSeF scam invoices. France switches on a comparable regime on 1 September 2026.

How a request at a pharmacy counter reaches a government ledger

KSeF became compulsory in phases — 1 February 2026 for taxpayers whose 2024 gross sales exceeded PLN 200 million, 1 April 2026 for the remaining VAT-registered businesses, and 1 January 2027 for micro-entrepreneurs. The production release, KSeF 2.0, went live with the first wave. Volume followed immediately: the Ministry of Finance reported over 87 million invoices from more than 345,000 entities in the first two months of mandatory operation.

In a clearance model, an invoice is not sent to a business. It is submitted to a central government platform, validated there, and then routed to a recipient identified only by the NIP written on the document. Three consequences follow, and none of them existed under invoicing by PDF and email:

  • Delivery is automatic and unconditional. The document lands in the recipient’s repository whether or not any transaction took place.
  • There is no accept-or-reject step. Nothing lets a recipient refuse a document before it is recorded against their tax number.
  • Corrective notes are gone. Errors, including a wrong NIP, are fixed only by the issuer raising a corrective invoice to zero. The recipient cannot correct a document issued against them.

A recipient can hide an unwanted document from their own view of the system. That is a display setting — reversible, invisible to the issuer, and it changes nothing about the document’s existence.

The video, and what happened to the man who filmed it

The pharmacy visit was staged. Tomasz Sidorczuk, a community activist from Bielsko-Biała better known locally for campaigning on cycling infrastructure, filmed the whole thing and posted it to TikTok, where it passed a million views inside a day and reached roughly 4.5 million by the end of the month.

Two facts about the incident matter more than the stunt. The invoice was never generated — the pharmacist declined to issue it. And the tax at stake was 89 groszy, under a quarter of a euro.

On 26 February 2026, Sidorczuk was questioned at the Silesian Customs and Tax Office in Katowice and charged with incitement to issue an unreliable invoice. He denies it and has said that if the case reaches court he intends to fight for acquittal; on the most recent reporting, charges have been presented but no indictment or verdict has followed.

His argument was never that the system can be broken into. It was that verification has quietly become the recipient’s job, at a volume nobody sized for. In a business processing thousands of documents a month, he said, it is bardzo łatwo przeoczyć fakturę wystawioną omyłkowo lub bez podstawy — “very easy to miss an invoice issued by mistake or without basis.”

One side says nothing is broken. The other is not arguing about the same thing.

Poland’s Ministry of Finance responded that the circulating material nie wskazuje na istnienie luki w KSeF — “does not indicate the existence of a gap in KSeF” — and gives no grounds to assert a risk connected with how the system functions. Public broadcaster Radio Kraków was blunter, treating the video as a stunt inflated beyond its worth, on the grounds that możliwość wystawienia faktury na dowolny NIP istniała od zawsze — “the ability to issue an invoice to any tax ID has always existed.”

Both statements are true, and both answer a question nobody asked. Writing someone else’s tax number on an invoice has never been hard. What changed is what happens afterwards.

Practitioners handling the inbound side describe the problem in operational terms rather than architectural ones. As Joanna Łuksza put it, wystawienie scamowej faktury nie zawsze jest proste do wykrycia — “issuing a scam invoice is not always simple to detect” — typically a document from a company the recipient has never dealt with, or for a transaction that never happened. Poland’s Ombudsman has raised a separate concern from a different direction: that the breadth of data gathered in KSeF may sit awkwardly with statutory protection of business secrets and with EU data-protection standards.

The disagreement dissolves once you separate issuing from delivery. Before KSeF, a fabricated invoice had to reach you — by post, by email, through a channel you controlled and could ignore. Under a clearance model it is validated by the state and placed directly into your tax records, with no point at which you can say no. The defence is right that issuing was always possible. It is answering an objection about delivery.

What Article 62 of the Fiscal Penal Code actually says

Coverage of the charges reported three different maximum penalties: three years, a floor of one year, and — attributed to a television journalist — up to eight. The statute settles it. Sidorczuk was charged under Article 18 § 2 of the Criminal Code, read with Article 20 §§ 1 and 2 and Article 62 § 2 of the Fiscal Penal Code of 10 September 1999 (consolidated text, Dz.U. 2025 poz. 633).

Article 62 § 2 provides for a fine of up to 720 daily rates, or imprisonment for a term not shorter than one year, or both. One year is the statutory floor, not the ceiling — and neither three years nor eight appears anywhere in the provision.

What sits immediately after it went unmentioned in the coverage entirely:

  • § 2a covers the same conduct where the tax arising from the invoice is of small value. It drops the one-year minimum, leaving a fine of up to 720 daily rates, or imprisonment, or both.
  • § 5 provides that in a case of lesser gravity, conduct under §§ 1–4 is punishable by a fine for a fiscal misdemeanour rather than as a fiscal offence.

The tax at issue was 89 groszy. Whether either provision applies here, and how incitement works where the invoice was never issued at all, are questions for the court and for a Polish fiscal-penal specialist — not conclusions to be drawn from reading a statute at a distance. But the gap between the reported exposure and the range the code sets out is wide enough that anyone working from the news figures is working from the wrong numbers.

What you can do when a scam invoice lands

KSeF 2.0 includes an abuse-reporting function: a business can flag a document it believes fraudulent for examination by the National Revenue Administration. Three limits are worth knowing before building a process around it.

  • Reports go one document at a time. There is no bulk submission.
  • The function is technical in character — the tax administration does not report back on what it finds.
  • You can track the status of your report. That is the extent of the visibility.

Where a wrong NIP is a genuine mistake rather than an attempt at fraud, the route is different and faster: contact the issuer, ask for a corrective invoice to zero, then a correctly addressed one. The distinction matters, because an abuse report aimed at what turns out to be a typo burns the only channel you have.

The failure mode worth designing against is mundane. Not a sophisticated attack — an invoice for a service nobody ordered, from a company nobody has dealt with, priced low enough and dated tightly enough to clear an approval queue on a busy week. The warning signs practitioners flag are unremarkable, which is exactly why they can be systematised: language errors in the service description, no reachable contact for the issuer, unusually short payment terms.

France goes live on 1 September 2026

France’s first obligation applies to every business regardless of size — the ability to receive compliant electronic invoices from 1 September 2026. Large and mid-sized enterprises must also issue from that date; smaller businesses follow on 1 September 2027. Invoices move through accredited platforms rather than one central state portal, so the architecture is decentralised in a way Poland’s is not. The property that produced the KSeF argument is the one both models share: a structured invoice addressed to your identifier arrives through a channel you do not control, and arrival is not consent.

Poland suspended financial penalties through the end of 2026, with enforcement beginning 1 January 2027. That has an underappreciated consequence for anyone watching from another jurisdiction — the incident rate visible today is the rate under conditions where mistakes are cheap. Belgium, live since 1 January 2026, moved to progressive penalties on 1 April 2026 once its tolerance period ended.

Two questions are worth settling before a mandate goes live rather than after. Who reviews inbound structured invoices, and does that person have authority to stop payment on a document already recorded against your tax number? And what internal signal separates a wrong-identifier error from an attempt at fraud, given that the remedies differ and only one of them is quick?

Frequently asked questions

Can I reject an invoice sent to my tax ID in KSeF?

No. Structured invoices are assigned to the buyer automatically on the basis of the NIP, with no accept-or-reject step, regardless of whether the transaction took place. You can hide the document in your own view of the system — reversible, and invisible to the issuer — but the document itself remains. Removal requires the issuer to file a corrective invoice to zero.

What should I do if a fraudulent invoice appears in my KSeF account?

Use the abuse-reporting function in KSeF 2.0 to flag it for the National Revenue Administration, one document at a time. If it looks like a simple error rather than fraud — a mistyped NIP, most often — contact the issuer first and ask for a correction to zero, which is faster. Pay nothing you cannot trace to a real order.

Does an invoice in my KSeF account mean I owe the money?

An invoice is a document, not proof of a debt. The obligation comes from the underlying transaction. The real risk is operational rather than legal: a document sitting in your records can be paid by mistake in a busy approval queue, and it still has to be handled correctly for VAT and reporting purposes. For a specific document and a specific exposure, take it to a tax adviser rather than a checklist.

Will France’s system work the same way as KSeF?

Not identically. France routes invoices through accredited platforms rather than a single central state portal. What carries across is that structured invoices addressed to your identifier arrive automatically through a channel you do not control — which is what makes the Polish experience worth reading before 1 September 2026.

When do penalties start in Poland?

Financial penalties for KSeF breaches are suspended through the end of 2026, with enforcement beginning 1 January 2027. That makes the rest of 2026 the window for fixing processes while errors are still cheap.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base, What happened with...

E-Invoicing vs E-Reporting: Two Systems, Not One

E-invoicing is an exchange: a supplier sends a structured document to a buyer so the buyer can book it and pay it. E-reporting is a transmission: a taxpayer sends fiscal data to a tax authority so the authority can cross-check it. Different recipient, different payload, different deadline, different consequence when it fails. They are two flows that happen to be derived from the same source document.

They get conflated because one service provider usually sells both, and because in some countries the same API call does both. But they are independent axes. Sweden, Finland and Norway have mandatory invoice exchange over Peppol with no tax authority controls involved at all — mandatory e-invoicing, zero e-reporting. Meanwhile India’s mandate is routinely called “e-invoicing” and its output is frequently an emailed PDF. Getting the distinction right determines what you build.

The two flows, side by side

Under ViDA — Council Directive (EU) 2025/516, the adopted text — the two flows are defined in different chapters of the VAT Directive, and every parameter differs.

  • Recipient. E-invoicing: the buyer. E-reporting: the tax authority that issued the VAT number used for the transaction (Article 262(2)).
  • Payload. E-invoicing: the invoice, complying with EN 16931 by default (Article 218(3)). E-reporting: ten data points (Article 264).
  • Deadline. E-invoicing: within ten days of the chargeable event (Article 222). E-reporting: at the moment the invoice is issued or should have been (Article 263(1)).
  • Who acts. E-invoicing: the supplier. E-reporting: the supplier and the customer, within five days of receiving the invoice — unless the member state waives it (Article 262(4)).
  • Harmonisation. E-reporting for cross-border is identical in every member state, with no possibility of requesting additional data. Domestic e-reporting is whatever each member state decides (Article 271b(4)).

One document, two consumers, and the consumers want different things. There is also a third: the ERPB’s 2016 working group report defines a Request To Pay as a subset extracted from the invoice, carrying the minimum needed to initiate payment plus a link back to the underlying invoice — and it notes that this message usually contains no tax details and no line items at all. Three parties, three data sets, one source document.

The buyer gets the invoice. The authority gets ten fields.

The concrete version comes straight from Article 264 as replaced by ViDA. From 1 July 2030, for an intra-Community supply, what gets transmitted to the tax authority is Article 226 points 1 to 4, 6, 7, 8, 11, 16 and 17, plus 11a where applicable. Ten data points.

Not on that list: point 5, the full name and address of both parties. The authority resolves identity from the VAT numbers via VIES; it doesn’t need the street. Also not on the list, for the supplier: the VAT rate and the VAT amount — an intra-Community supply is exempt, so there is no rate to report. The customer’s report of the same transaction does carry the rate and the amount, because in the customer’s country the transaction is taxable. Supplier reports ten fields, customer reports twelve, same transaction.

Now compare that with what the buyer needs from the same document: line-level descriptions and quantities, the purchase order reference, the delivery address, payment terms, the supplier’s bank details, an accounting cost code for coding it to the right centre. Almost none of that is reportable. It is the entire reason the invoice exists.

The two data sets overlap. Neither contains the other.

Different failure modes, and this is where it gets expensive

If e-invoicing fails, the buyer doesn’t get an invoice, and eventually somebody calls somebody. It’s a commercial problem with a commercial remedy.

If e-reporting fails, the tax consequences are structural. ViDA amends Article 138(1a) so that the exemption for an intra-Community supply does not apply where the supplier has not met the Articles 262 and 263 transmission obligation, or where the data transmitted doesn’t contain the correct information required by Article 264 — unless the supplier can duly justify the failure to the competent authorities. Miss the report, and a zero-rated cross-border supply becomes a taxable one.

On the other side, ViDA adds a subparagraph to Article 168 letting member states provide that a customer may deduct or reclaim VAT only where it holds an electronic invoice issued in accordance with Article 218(3). Note the scope: that option attaches to transactions subject to the domestic reporting requirements of Article 271a(1). It is an option, not an obligation, and it is national.

So the same missing message costs a late payment on one plane and an exemption on the other. Systems that treat the report as a downstream side effect of a successful invoice send are mis-modelling the risk — the report has the sharper teeth.

Where the tax authority actually sits: the corner models

The ERPB’s 2016 report categorises e-invoicing solutions by the number of intermediary platforms in the presentation flow: Supplier Direct, where the supplier runs the whole lifecycle and the payer comes to the supplier’s portal; Buyer Direct, where suppliers post into a platform on the buyer’s side; the three-corner network, where one service provider sits between both parties; and the four-corner network, where each party has its own provider and flows are routed between the two platforms.

The tax authority is not a corner in any of them. That isn’t an oversight in 2016 — it’s the definition. E-invoicing was a two-party exchange, and intermediaries were counted by how many sat in the presentation path.

When tax authorities arrived, the industry had to invent a fifth corner, and the name it settled on gives the game away: DCTCE, Decentralized CTC and Exchange. Two functions, named separately, in one acronym. France’s model is drawn as a Y for the same reason — two branches for exchange (issuing and receiving through approved platforms) and a third branch for e-reporting, submitting invoice, transaction and payment data to the tax authority through the public portal.

And here the vendor pages that inspired this article contradict each other outright. Some describe the five-corner model as one where invoices must first pass through a government platform to be validated and registered before continuing to the buyer. Others describe the same model as one where a copy is sent to the tax authority before or immediately after delivery, while the invoice reaches the buyer through their own access point. Those are different architectures, and the difference is load-bearing: one commentary notes the decentralised version is gaining ground precisely because pre-clearance submission undermines established billing processes and makes the authority’s portal a single point of failure.

Both descriptions are accurate — about different systems. Clearance (the authority is in the exchange path, and the invoice isn’t valid until it comes back) and near-real-time reporting (the authority gets a copy on a separate leg) are distinct designs. ViDA mandates the second for intra-EU: transmit at the time of issue. It does not put the authority between supplier and buyer.

The mandates called “e-invoicing” that are really e-reporting

Two of the clearest examples come from implementation guides rather than marketing pages.

India. Sigitek’s SAP e-invoicing solution documentation describes the flow: every SAP billing document is pushed as JSON to the Invoice Registration Portal via an authorised GSP; the IRP checks the IRN against the GST system’s central registry for uniqueness, signs the invoice data, adds a QR code and returns the digitally signed JSON with the IRN to SAP; the IRP then shares the signed data with the GST system and the E-Way Bill system, and GSTR-1 is auto-populated on a T+1 basis. The buyer appears nowhere in that flow. The last step in the vendor’s own architecture diagram is “Print or Email Invoice”. The structured data goes to the government; the buyer gets a printout with a QR code on it.

Greece. SAP’s August 2024 implementation guide describes the same shape. Invoices route through a certified service provider to myDATA, which returns a MARK, a UID and an authentication code — and the requirement is then that the QR code, MARK, UID, authentication code and the provider’s name are printed on the invoice. Real-time submission, rendered as ink.

In both cases the mandate is an e-reporting mandate wearing an e-invoicing label. The tell is simple: ask who receives the structured data. If the answer is “the tax authority, and the buyer gets a PDF”, that’s e-reporting. The exchange plane hasn’t been digitised at all.

The one place they genuinely couple

The flows are separable, but not independent — and the dependency runs one way.

The new Article 217, applying from 1 July 2030, defines an electronic invoice as one issued, transmitted and received in a structured electronic format allowing automated processing — “at least in relation to the data referred to in Articles 262 and 271b”. Articles 262 and 271b are the reporting articles. The reporting requirement is what sets the structured minimum for the invoice. ViDA’s recital 11 says it plainly: the invoice should contain, in structured format, all the data that has to be transmitted to the authority, so that transmission can be automated from it.

That single qualifier explains two things people find confusing. It’s why hybrid formats like ZUGFeRD and Factur-X survive — the reportable data is in the XML, so the PDF layer is legally irrelevant. And it’s why e-reporting is driving e-invoicing rather than the other way round: the tax authority’s data needs define the floor of the format your buyer receives. Not the buyer’s needs. Not yours.

Meanwhile the old periodic report dies. ViDA deletes Articles 265 to 271 from 1 July 2030 — recapitulative statements disappear, replaced by transaction-by-transaction transmission. That’s the actual reform: not new reporting, but the same reporting moved from monthly batch to per-transaction, which is only affordable if it’s derived automatically from a structured invoice.

How to tell which one you’re being sold

Four questions cut through most vendor pages:

  • Who receives the structured data? Buyer, authority, or both. “Both” is a five-corner or DCTCE architecture. “Authority only” is e-reporting with an e-invoicing label.
  • Is the authority in the path or beside it? Clearance means the invoice isn’t valid until the platform returns an identifier. Reporting means a copy travels separately and the invoice is valid regardless.
  • What happens if the report fails but the invoice arrives? If the answer is “nothing”, the flows are decoupled. If it’s “the exemption goes”, you’re inside Article 138(1a).
  • Which data set is being mapped? Ten header fields is a reporting integration. Around 170 EN 16931 business terms is an invoicing integration. They’re different projects with different costs.

Frequently asked questions

Is e-reporting just e-invoicing sent to the government?

No. Under ViDA it’s a defined subset — Article 226 points 1 to 4, 6, 7, 8, 11, 16 and 17 — transmitted per transaction on its own leg, without the parties’ names and addresses. In some national systems a full invoice copy does go to the authority, which is why the misconception is durable, but the EU cross-border design transmits data, not documents.

Can you have e-invoicing without e-reporting?

Yes, and several countries do. Invoice exchange over Peppol is mandatory in Sweden, Finland and Norway, and it isn’t a CTC model because there are no tax authority controls involved. Mandatory structured exchange, no fiscal transmission.

Can you have e-reporting without e-invoicing?

Yes — that’s what India and Greece currently demonstrate at the buyer’s end, where the structured data reaches the tax authority and the counterparty receives a printed or emailed document carrying a QR code.

Do both the supplier and the buyer have to report under ViDA?

By default yes: the supplier at the time of issue, the customer within five days of receiving the invoice. But Article 262(4) lets member states drop the customer-side obligation, and ViDA’s recitals explain why — the customer’s report exists to cross-check the supplier’s, so a member state that already has assurance the supplier will report can waive it.

Does ViDA make my country’s clearance system illegal?

No. Member states with a domestic real-time transaction-based reporting obligation in place on 1 January 2024 have until 1 January 2035 to align those domestic systems, and Article 273 lets existing general reporting obligations continue until a compliant system replaces them. The convergence is real but slow, and it applies to domestic flows — the intra-EU leg is harmonised from 2030.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base

From VAT Return to Continuous Transaction Controls: Why Report-Later Is Ending

On 1 July 2030, Council Directive (EU) 2025/516 deletes Articles 265 to 271 of the VAT Directive. That single provision abolishes the recapitulative statement — the periodic summary of intra-Community supplies, filed after the fact, that has been the archetype of reporting later for three decades. In its place: transmission of transaction data at the moment the invoice is issued.

That is the whole shift in one legal fact. Not new reporting — the same reporting, moved from monthly batch to per-transaction, which is only affordable if it’s derived automatically from a structured invoice. The stated reason is fraud. The Commission’s own evidence for that reason is weaker than almost anyone selling this will tell you, and it’s worth understanding why before you build to it.

What “report later” actually was

The old model has a retronym now — periodic transaction controls, PTC — but its defining feature was never the periodicity. It was that the tax authority saw nothing until it asked.

The 2016 edition of the E-Invoicing and Retention in Europe compendium, compiled by Peters, Schönberger & Partner across 22 European countries, is a complete snapshot of that world. The recurring question in every chapter is how a business ensures authenticity of origin and integrity of content — and the recurring answer is business controls creating a reliable audit trail, matching the invoice against purchase orders and other existing documents. The taxpayer builds the evidence. The taxpayer keeps the evidence, for five years in Greece and Poland, eleven in Croatia, up to 22 in Austria for immovable property. The authority arrives later, if at all.

The clearest expression of the old logic is a small Czech rule the compendium records: invoices may be stored outside the Czech Republic only where there is continuous remote access, and after prior notification to the tax authority. Read that carefully. The authority wanted continuous access to the archive — a standing right to reach the data, exercised on demand. Continuous transaction controls invert it: the authority no longer reserves a right to come and look, because the data arrives on its own.

Same objective, opposite mechanism. Which is why “faster reporting” undersells it.

Nobody called it PTC at the time

Worth stating plainly, because it dates the vocabulary: neither “continuous transaction controls” nor “periodic transaction controls” appears anywhere in the 2016 PSP compendium, in the Euro Retail Payments Board’s 2016 working group report on e-invoicing solutions, or in Billentis’s 2017 business case. Several hundred pages, written by specialists at the centre of European e-invoicing, and the terms are simply absent.

PTC is a retronym. It exists to have something to contrast CTC against, the way “acoustic guitar” only became necessary once electric ones existed. In 2016 this wasn’t a model with a name. It was just how VAT worked.

One detail cuts against the neat chronology, though. Greece’s 2016 answer on ensuring authenticity already listed, alongside signatures and EDI, both special safe appliances (electronic tax machines) and clearance of sales transactions through a payment service provider. The country that would go on to build myDATA was already describing clearance mechanisms in a post-audit questionnaire. The shift was visible before it had a label.

What replaces it, and when

The mechanics under ViDA are precise, and the dates are the deliverable:

  • Invoice deadline compresses. For intra-Community supplies and reverse-charge transactions, the invoice must be issued within ten days of the chargeable event (Article 222) — down from the fifteenth day of the following month.
  • The report leaves at issue. Data is transmitted per individual transaction at the moment the invoice is issued or should have been (Article 263(1)). Self-billed invoices get five days. The customer reports within five days of receiving the invoice, unless the member state waives it (Article 262(4)).
  • The payload is fixed. Ten data points for the supplier — Article 226 points 1 to 4, 6, 7, 8, 11, 16 and 17, plus 11a where applicable (Article 264). Identical in every member state, with no possibility of requesting additional data.
  • Missing the report has teeth. Article 138(1a) removes the exemption for an intra-Community supply where the supplier hasn’t met the transmission obligation, or where the data transmitted doesn’t contain the correct information — unless the failure can be duly justified to the competent authorities.
  • Summary invoices survive, narrowed. Article 223 keeps periodic invoices where VAT on the different supplies becomes chargeable in the same calendar month, issued within ten days of month end — and lets member states exclude them entirely in fraud-sensitive sectors. Note this: the original ViDA proposal abolished summary invoices outright. The adopted text kept them. Commentary written from the draft still says otherwise.
  • Domestic systems get five more years. Member states with a domestic real-time transaction-based reporting obligation in place on 1 January 2024 have until 1 January 2035 to align.

Reporting later doesn’t disappear so much as shrink to a residue: the VAT return itself survives, and Article 273 explicitly lets member states keep national tools like SAF-T alongside the real-time obligations. What dies on 1 July 2030 is the periodic transaction listing.

The official case for it — and where the numbers don’t hold

ViDA’s recital 3 makes the argument: the VAT gap was estimated at €93 billion across the Union in 2020, a significant part of it fraud, and in particular intra-Community missing trader fraud, estimated at around €40 to €60 billion. Recital 4 supplies the mechanism: transaction-by-transaction transmission lets administrations cross-check data, increases control capacity, and deters non-compliance.

Then compare that with what the Commission has published since.

The VAT gap in Europe — report 2025, released on 11 December 2025, puts the EU VAT compliance gap at €128 billion for 2023 — 9.5% of the total VAT liability, against total VAT revenue of €1,223 billion. That’s an increase of 1.6 percentage points on 2022, and the Commission’s own Mind the Gap report describes it as reversing the progress observed during the pandemic. Over the longer run the picture is better: 11.1% in 2019 down to 9.5% in 2023. Both statements are true, which is why you’ll see the same report cited as evidence of success and of failure.

The harder problem is the fraud number. A Commission-commissioned study estimating the MTIC gap at EU level using Intrastat mirror-trade statistics put it at between €12.5 billion and €32.8 billion annually across 2010 to 2023 — an average annual loss of 1.2–3.1% of actual VAT revenue. Set that beside the directive’s own €40–60 billion. The upper bound of the Commission’s later estimate is below the lower bound of the figure in the recital.

And the study’s conclusion is more awkward still: the MTIC gap has been broadly stable over time, which the Commission reads as suggesting that factors other than MTIC fraud drive the fluctuations in the VAT compliance gap. If carousel fraud is stable and the gap moves anyway, then the gap is mostly being moved by something CTC doesn’t target — bankruptcies, insolvency, administrative error, real-terms revenue decline. The 2025 report’s own context supports that: between 2021 and 2023 theoretical VAT liability rose 17.3% while actual revenues grew 14.4%, and bankruptcies rose across most of the EU.

Three more figures worth holding:

  • The two best-performing member states run no CTC mandate. Austria’s 2023 compliance gap is about 1.0%, Finland’s about 3.0% — the lowest in the EU. Neither has continuous transaction controls. Whatever they’re doing works without it.
  • The gap is concentrated. Around 75% of the EU compliance gap comes from six countries: France, Germany, Italy, Poland, Romania and Spain. This is not an EU-wide compliance problem being solved with an EU-wide instrument.
  • The policy gap dwarfs the compliance gap. Revenue forgone through reduced rates and exemptions ran to roughly €743 billion in 2023 — around six times the entire compliance gap. The largest hole in EU VAT revenue is a deliberate policy choice, not fraud.

None of that makes CTC pointless. Faster data genuinely does help administrations that are under-resourced rather than under-informed, and the Commission’s own analysis attributes diverging national trends partly to digital reporting reforms. But the honest summary is that the reforms have yet to reverse the recent increase in the EU-wide gap, and the specific fraud they target is a smaller and steadier problem than the directive that targets it asserts. Anyone quoting €40–60 billion in 2026 is quoting a recital, not a measurement.

Why it’s happening anyway

Because the argument for CTC was never really only about fraud — it’s about latency, and latency is what the sources actually show changing.

Look at what the working implementations do. SAP’s August 2024 guide for Greek e-invoicing describes real-time submission through a certified service provider, with myDATA returning a MARK, a UID and an authentication code that must then be printed on the invoice. Sigitek’s SAP solution for India pushes every billing document as JSON to the Invoice Registration Portal via an authorised GSP, which validates the reference number against the GST system’s central registry, signs the data, returns it with a QR code, forwards it to the GST and E-Way Bill systems — and auto-populates the GSTR-1 return on a T+1 basis.

That last clause is the point. The return isn’t abolished; it’s pre-filled. Once the authority holds the transaction data, the periodic filing stops being a declaration the taxpayer composes and becomes a statement the authority proposes. That is a different relationship, and it’s a far more attractive prize for a tax administration than any individual fraud case.

It’s also why e-reporting drives e-invoicing rather than the reverse. The new Article 217 defines an electronic invoice as one in a structured format allowing automated processing — “at least in relation to the data referred to in Articles 262 and 271b”, the reporting articles. Recital 11 is explicit that the invoice should carry all the data to be transmitted, in structured format, so the transmission can be automated from it. The authority’s data needs set the floor for the document your buyer receives.

What to do about it

Three things follow, regardless of what you think of the fraud case.

Model latency, not frequency. The design constraint isn’t “report more often”. It’s that the report is emitted by the act of invoicing, synchronously, with a legal consequence on failure. Any architecture that treats reporting as a nightly job is building the wrong thing.

Assume the return gets pre-filled. India already does it on a T+1 basis. If your reconciliation process assumes you are the authoritative source of your own VAT position, that assumption has a shelf life.

Watch the domestic layer, not the EU one. The intra-EU set is ten fields, fixed everywhere from 2030. Domestic reporting is optional for member states and its content is defined nationally under Article 271b(4) — that’s where the divergence and the cost live, and it runs to 2035.

Frequently asked questions

What are continuous transaction controls?

Any regime where transaction data reaches the tax authority at or near the moment of the transaction, rather than in a periodic filing afterwards. It covers both clearance models, where the authority validates the invoice before it’s valid, and real-time reporting, where a copy or subset travels to the authority on a separate leg. ViDA mandates the second for intra-EU supplies from 1 July 2030.

Is the VAT return being abolished?

No. ViDA abolishes recapitulative statements — the periodic listing of intra-Community transactions — from 1 July 2030 by deleting Articles 265 to 271. The VAT return itself remains, and Article 273 lets member states keep national reporting tools such as SAF-T. What changes is that the return increasingly gets pre-populated from data the authority already holds.

Does CTC actually reduce VAT fraud?

The evidence is more equivocal than the marketing. ViDA’s recital estimates missing trader fraud at €40–60 billion a year; a Commission study using mirror-trade statistics puts the MTIC gap at €12.5–32.8 billion and finds it broadly stable across 2010–2023. The EU compliance gap rose to €128 billion in 2023 while digital reporting was spreading. Digital reporting is one of several factors the Commission credits for diverging national trends — but the causal claim is not settled, and the two lowest-gap member states have no CTC at all.

When does my country switch?

For intra-EU B2B, 1 July 2030 everywhere. Domestically it varies: member states have been free to mandate e-invoicing without a derogation since 14 April 2025, which is why national mandates are arriving first, and those with a real-time domestic system already in place on 1 January 2024 have until 1 January 2035 to converge.

Do summary invoices still work?

Yes, with limits. Article 223 as amended allows periodic invoices covering supplies whose VAT becomes chargeable within the same calendar month, issued within ten days of month end, and lets member states exclude them in fraud-sensitive sectors. The ViDA proposal would have removed them entirely; the adopted directive did not.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base

How Many Fields Are in an EU E-Invoice? 10, 17 or 176?

All three, depending on which layer is asking. VAT law lists 15 mandatory particulars in Article 226 of the VAT Directive, rising to 17 on 1 July 2030. ViDA’s digital reporting will transmit exactly 10 of those 17 to the tax authority for a cross-border supply. EN 16931’s core invoice model defines around 170 business terms — 176 by the most-cited count, and even that figure is contested — of which roughly 25 are mandatory. And the UBL syntax that carries all of it has no published field count at all.

That gives three numbers and one non-answer to “what’s on an invoice” — and the part that breaks data models is that the sets are not nested. Each layer makes something mandatory that the others don’t ask for. There is no superset invoice to model against.

The three layers, and what each one is actually for

The confusion is structural, not sloppy. Each layer was defined by a different body answering a different question.

  • The legal invoice — Article 226 of the VAT Directive. Question: what must a document say to establish a VAT position? Roughly 15–17 particulars, and it is a closed list.
  • The reportable set — Article 264 as replaced by ViDA. Question: what does the tax authority need transmitted? Ten data points for cross-border B2B, fixed EU-wide.
  • The core invoice — EN 16931, built by CEN/TC 434 under Directive 2014/55/EU. Question: what must two systems agree on to process an invoice automatically across borders? Around 170 business terms.
  • The commercial invoice — the UBL 2.1 or UN/CEFACT CII document that actually gets sent. Question: what could a trading document ever need to carry? Effectively uncountable.

Only the first is law. The second is law about the first. The third is a standard the law now points to. The fourth is a container.

The legal layer: Article 226 is a closed list of 15, going to 17

Article 226 opens by saying that only the details it lists are required for VAT purposes. The word “only” is doing real work: this is a ceiling, not a floor. The European Commission’s own explanatory notes on the 2010 invoicing rules make the point explicitly when discussing exchange rates — a requirement to state the conversion method would be a detail above those required in Article 226, and therefore not permitted.

The list runs to 15 numbered points: issue date, sequential number, the supplier’s VAT number, the customer’s VAT number where they’re liable, the full name and address of both parties, quantity and nature of the supply, the supply date, the taxable amount per rate, the VAT rate, the VAT amount, exemption or reverse-charge references, and the special-scheme mentions. Points 7a (cash accounting) and 11a (“Reverse charge”) sit inside that structure as insertions rather than extensions.

The floor is much lower than most product teams assume. Under Article 226b, a simplified invoice needs five details — issue date, identification of the supplier, identification of the type of goods or services, the VAT amount payable or the information needed to calculate it, and, for a corrective document, a reference to the original. The fifth is conditional, so the practical minimum is four. Article 220a makes simplified invoices available where the invoice does not exceed EUR 100.

Council Directive (EU) 2025/516 — ViDA — adds two points with effect from 1 July 2030: point 16, the sequential number of the corrected invoice on a corrective invoice, and point 17, the supplier’s bank account numbers, virtual account numbers, or any other identifier unambiguously identifying the accounts the invoice can be paid into. Point 11a also gains a “triangular transaction” mention. Seventeen points, from a single date.

Be careful with secondary sources here. A large amount of published commentary still describes the ViDA proposal, which added three points — the third being the payment due date — with effect from 2028. The adopted directive contains two, from 2030. If your data model has a mandatory payment-due-date field because of ViDA, it was built from a draft.

The reporting layer: ViDA transmits 10 of the 17, and the buyer’s name isn’t one

This is the number almost nobody has, because it requires reading Article 264 as replaced by ViDA rather than a summary of it. From 1 July 2030, for an intra-Community supply under Article 138(1) and for supplies where the customer is liable under Articles 194 to 197, the data transmitted is: Article 226 points 1 to 4, 6, 7, 8, 11, 16 and 17 — plus 11a where applicable. Ten data points, eleven with the reverse-charge mention.

What’s missing from that list is more instructive than what’s in it:

  • Point 5 — the full name and address of both parties. Not reported. The VAT identification numbers are, and the authority resolves identity through VIES.
  • Points 9 and 10 — the VAT rate and the VAT amount. Not reported by the supplier. An intra-Community supply under Article 138 is exempt, so there is no rate to report.

The asymmetry goes further. For intra-Community acquisitions under Article 20, Article 264(c) requires points 1 to 4, 6, 7, 8, 9, 10, 11, 16 and 17 — twelve. The acquirer reports the rate and the amount that the supplier didn’t, because in the acquirer’s country the transaction is taxable. Supplier and customer report the same transaction with different field sets. Any model that assumes one invoice produces one report will be wrong on both counts.

Two more constraints matter for anyone building this:

Cross-border is fixed; domestic is not. Recital 18 of ViDA states the reportable data should be the same in every member state, with no possibility for them to request additional data. But Article 271b(4), governing optional domestic digital reporting, says member states determine the data to be transmitted themselves. So there is no single reporting layer — there is one harmonised set for intra-EU, and up to 27 national sets for domestic. Greece’s myDATA already illustrates the shape: SAP’s implementation guide for Greek e-invoicing records the XML as carrying invoice type, total amount, net amount, VAT category, classification category and classification type, with the platform returning a MARK, a UID and a QR code that then have to be printed back onto the document.

The structured requirement attaches to the reportable subset, not the document. The new Article 217 defines an electronic invoice as one issued, transmitted and received in a structured electronic format allowing automated processing — “at least in relation to the data referred to in Articles 262 and 271b”. That qualifier is why hybrid formats survive: ZUGFeRD and Factur-X are compliant because the reportable data sits in the XML, whatever the PDF layer does.

The core layer: EN 16931, and why nobody agrees on the count

The directive asked CEN to build a semantic data model of the core elements of an electronic invoice. The Euro Retail Payments Board’s 2016 working group report quotes the directive’s own definition of those core elements: the essential information components an e-invoice must contain to enable cross-border interoperability, including what’s needed for legal compliance — to which the ERPB added, pointedly, that fiscal compliance is included too.

Ask how many business terms that produced and you get four answers. Material from CEN/TC 434’s own presentations describes about 160 elements in 33 element groups, with some 25 mandatory and 9 datatypes. Aleksandra Bal, writing in Forbes in January 2025, says over 160 semantic data fields. ValidateFin’s guide says approximately 170 business terms and business term groups. InvoStaq says 176. Nobody is lying: BT identifiers aren’t contiguous, business groups (BG) can be counted as fields or as containers, and the standard has been revised.

For a data team the useful number is the mandatory one — roughly 25 — because that’s the validation floor. Everything else is optional, conditional, or narrowed by whichever Core Invoice Usage Specification applies. CIUS restricts (Peppol BIS Billing 3.0 is a CIUS of EN 16931 on UBL 2.1); Extensions widen, and the European Commission maintains a registry of both. The German XRechnung Extension for the construction sector adds sub-invoice lines beneath a single invoice line and lets GAEB data ride along as an embedded XML attachment — an entire industry’s data model bolted onto the side of the core.

Here is the collision with the legal layer. EN 16931 makes fields mandatory that VAT law never asks for: CustomizationID (BT-24), ProfileID (BT-23) and BuyerReference (BT-10) are required for a valid Peppol BIS invoice and have no existence in Article 226 at all. They are routing and validation metadata. Article 226 says “only these”; the standard says “also these”. Both statements are true, because they are different instruments doing different jobs — and ViDA’s Article 218(4) confirms it by requiring member states to ensure e-invoices do two separate things: include the information required by the Directive, and respect the technical standards. Two tests, not one.

When they genuinely conflict, tax law wins over the technical standard. That’s the ordering to encode.

The commercial layer: UBL has no field count, and that’s the point

The UBL 2.1 Invoice element has roughly fifty direct children, and reading them tells you what layer you’re in. Alongside ID and IssueDate sit ProfileExecutionID, CopyIndicator, PricingCurrencyCode, PaymentAlternativeCurrencyCode, AccountingCostCode, LineCountNumeric and WithholdingTaxTotal. None of those is a VAT concept. Several aren’t an invoicing concept.

Asking for the total field count is an ill-posed question. UBL splits elements into cbc (common basic components — the leaves) and cac (common aggregate components — containers that expand recursively into addresses, parties, items, prices and tax categories, each drawn from a shared library used by every UBL document type, not just invoices). OASIS designed UBL as a generic interchange format to be restricted or extended per industry, aligned with ISO 20022 and built to carry invoice financing, factoring and letters of credit. The invoice is a projection of a much larger library, so the count depends entirely on where you stop expanding the tree — which is why no authoritative figure is published, and why claims of “thousands of fields” can’t be sourced to OASIS.

The practical consequence: Peppol BIS Billing 3.0 doesn’t ship its own XSD. It reuses the UBL 2.1 schema unmodified and layers Schematron rules on top. The constraint lives outside the syntax, because the syntax constrains almost nothing.

What the gap costs: a real mapping table

SAP Hellas’s August 2024 implementation guide for Greek e-invoicing contains the artefact most articles on this topic don’t have — an actual field mapping, ERP to tax-authority message. The proxy structure runs to around 170 distinct field names across eleven structures: header, B2G details, issuer, counter party, recipient, distribution details, payment details, line details (separately for SD and FI documents), taxes, summaries, VAT analysis and contract order details. The marker “NP” — not provided — appears more than 120 times.

That ratio is the story. The message schema carries slots for VAT_MEDIATOR, TRANSPORTER, SENDER, DISPATCH_ADVICE, LOT_NUMBER, ORDER_CODE, BANKS and MISCELLANEOUS_DATA, and for a normal Greek B2G invoice every one of them is empty. Meanwhile the fields that are populated pull data from places no invoice model would predict:

  • CPV codes. Required by the tax authority for B2G, maintained in table T604F, and mapped per material on the International Trade tab of the material master. The guide notes that for FI invoices to public bodies a material code and plant have to be maintained during posting purely so the CPV code can be derived — a pure accounting document forced to carry logistics master data.
  • The contracting authority. Carried by a special partner record whose Name1 through Name4 fields hold the authority name, authority code, contract type code and contract reference code. Four legal identifiers stuffed into four name fields, because the data model had nowhere else to put them.

None of those fields is in Article 226. None is in the ViDA reportable ten. Two of them aren’t in EN 16931’s core. They are the expensive ones anyway, because field-level mismatches surface as exceptions — and exceptions are where the cost lives. Billentis’s 2017 business case puts typically 20–30% of all invoices into exception handling under scan-and-capture or image-PDF workflows, against Finnish State Treasury estimates of about 10 euros to process an invoice semi-automated and about 1 euro fully automated.

Why the layers don’t nest, and how to model them anyway

Take four fields and check them against each layer:

  • Buyer name and address — required by Article 226(5), required by EN 16931, not reported under ViDA.
  • CustomizationID (BT-24) — required for a valid Peppol BIS invoice, absent from VAT law entirely.
  • Supplier IBAN — absent from VAT law until 1 July 2030, then mandatory under Article 226(17), and reported.
  • CPV code — not in VAT law, not in the EN 16931 core, mandatory for Greek B2G.

No layer contains another. Which gives four concrete rules:

Don’t build a canonical superset invoice. There is no schema that is simultaneously the legal minimum, the reportable set, the interoperable core and the syntax. Model the semantics once and project into each target, rather than growing one table until it satisfies everybody.

Model the legal set as the closed list it is. Seventeen points from July 2030, sourced from Article 226 — not inherited from whatever XSD your access point handed you.

Treat the reporting set as two things, not one. Ten fixed fields for intra-EU, set by Article 264 and identical in every member state. And a per-country data set for domestic reporting, defined nationally under Article 271b(4), which means the domestic reporting layer is a configuration surface, not a constant.

Bind to syntax at the edge. EN 16931 is syntax-neutral by design, with UBL 2.1 and UN/CEFACT CII as the two official bindings and lossless conversion between them. Model against the semantic layer; serialise late.

Frequently asked questions

Is EN 16931 the same thing as UBL?

No. EN 16931 is a semantic data model — it defines what an invoice means. UBL 2.1 is one of two XML syntaxes officially bound to it; UN/CEFACT CII is the other, used by ZUGFeRD, Factur-X and optionally XRechnung. The same EN 16931 invoice can be expressed in either, and converted between them without loss.

How many EN 16931 fields are actually mandatory?

Around 25 of roughly 160–176, depending on whose count you use. But a CIUS can make an optional core field mandatory in a given country or network, so the real answer is: 25 plus whatever your target CIUS adds. Validate against the CIUS, not the core.

Does a VAT-compliant invoice automatically pass EN 16931 validation?

No, and the reverse is also false. A paper invoice carrying every Article 226 detail is legally valid and fails EN 16931 outright. An EN 16931 invoice can be technically conformant while missing something national tax law requires. ViDA’s Article 218(4) treats these as two separate tests precisely because they are.

What exactly will ViDA report to the tax authority?

For an intra-EU B2B supply from 1 July 2030: Article 226 points 1 to 4, 6, 7, 8, 11, 16 and 17, plus 11a where relevant — ten data points, eleven with the reverse-charge mention. Not the parties’ names and addresses. Not the VAT rate or amount, for exempt intra-Community supplies. The customer’s report of the same transaction carries twelve.

Which layer wins when they conflict?

Tax law, over any technical standard. In practice the sharper version of the question is which representation wins inside a hybrid invoice — and in Germany, the structured part governs where the PDF and XML disagree.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base

Is a PDF an E-Invoice? EU Law Has Two Definitions

Both answers are correct, and which one applies depends on which directive is asking. Under the VAT Directive, an electronic invoice is one issued and received “in any electronic format” — a PDF qualifies. Under Directive 2014/55/EU, which governs invoicing to the public sector, an e-invoice must arrive in a structured format that a machine can process on its own — a PDF does not qualify. The same file can therefore be a fully valid e-invoice when you email it to a customer and not an e-invoice at all when you send it to a public authority in the same country on the same afternoon.

That gap is not a drafting accident. It exists because the two laws are asking different questions, and it is scheduled to close on 1 July 2030 — earlier in the member states that have already moved.

The two definitions, side by side

Article 217 of the VAT Directive (2006/112/EC, as amended by Directive 2010/45/EU) defines an electronic invoice as one containing the information the Directive requires, issued and received in any electronic format. It says nothing about structure, syntax, or machine readability. A scanned image, an emailed PDF, an EDIFACT message, and a UBL XML file all sit in the same legal box.

Directive 2014/55/EU defines it differently: an invoice issued, transmitted and received in “a structured electronic format which allows for its automatic and electronic processing”. The Euro Retail Payments Board’s 2016 working group report spelled out what that phrase does in practice — the invoice has to enable fully digital processing with no human copy-pasting or retyping data. That is a technical test, not a legal-form test, and a PDF fails it.

Why the VAT rule ignores format

VAT law does not ask whether a machine can read your invoice. It asks whether you can prove the invoice is genuine and unaltered. Article 233 requires authenticity of origin, integrity of content, and legibility from the moment of issue until the end of the storage period — and it lets you satisfy that through business controls creating a reliable audit trail, an advanced or qualified electronic signature, or EDI.

Business controls are the low-tech option, and they are why PDFs pass. In Austria, for instance, the requirement is an internal control procedure with an audit trail — matching the invoice against existing business documents such as the purchase order. Nothing about that requires structured data.

The 2016 edition of the E-Invoicing and Retention in Europe compendium, compiled by Peters, Schönberger & Partner with local tax practitioners in each market, asked the same question in 22 European countries: does an electronic invoice have to be in a structured data format such as XML? Every one of the 22 answered no, and every one confirmed PDF or PDF/A was acceptable for both issuance and storage. The nuances were small: Hungary restricted formats to a whitelist (which included .pdf) and required a digital signature or EDI, Romania then required an extended digital signature based on a qualified certificate and noted XML and PDF were merely preferred, and the UK’s HMRC listed EDI, XML, comma-delimited ASCII and PDF as examples without mandating any.

Retention rules were the opposite of harmonised. The same compendium recorded periods ranging from five years (Greece, Poland) to eleven (Croatia), with Austria stretching to 22 years for immovable property and Belgium to 15 for investment goods. France added a format condition that still catches people: electronic invoices must be archived in their original format for three years, within an overall ten-year retention period.

Why the public-procurement rule doesn’t

Directive 2014/55/EU exists to make invoices flow into government finance systems without anyone rekeying them. It commissioned CEN to build EN 16931 — a semantic data model for the core elements of an invoice, with a list of compliant syntaxes (UBL and UN/CEFACT CII, both XML). Per the European Commission’s own compliance roadmap, all central contracting authorities had to be able to receive and process EN 16931-compliant invoices by 18 April 2019, with an optional 12-month extension pushing sub-central authorities to 18 April 2020.

Here is the caveat almost every summary skips: the Directive obliges the contracting authority to receive and process compliant e-invoices. It does not, by itself, oblige the supplier to send them. Whether you must issue structured invoices to the public sector is a question of national transposition — and many member states went further than the Directive required. Greece is the clear case: Law 4601/2019 (articles 148–154) transposed the Directive, and ministerial decision ΚΥΑ 63446/2-6-2021 then defined the national B2G invoice format, with GSIS acting as the national Peppol authority.

Legal but useless: what the format actually costs

The VAT-legal PDF and the structured e-invoice are separated by roughly an order of magnitude in processing cost, and the sources are unusually specific about it.

Billentis’s 2017 business-case report cites Finnish State Treasury estimates that an incoming paper invoice costs the receiving company 30–50 euros. Moving to electronic invoicing cuts that to about 10 euros with a semi-automated process — and to about 1 euro when the process is fully automated. The PDF lands you in the middle tier. The structured invoice is what buys the bottom one.

Why the middle tier is expensive is not mysterious. Under a scan-and-capture or image-based PDF workflow, Billentis reports that typically 20–30% of all invoices have to be handled as exceptions in one form or another, which is where the processing cost concentrates. When a recipient feeds an emailed PDF into the same capture pipeline it uses for scanned paper, the report notes the resulting data quality is only slightly better than with paper. The invoice arrived instantly and cost nothing to post — and then joined the same queue.

The report’s modelled recipient case (an industrial company with 5,000 employees, staff costed at 60 euros per hour) puts full paper processing at 17.60 euros per invoice against 6.40 euros for an electronic, automated flow — a 64% saving. On the issuing side the same case shows 11.10 euros against 4.50, or 59%. That distribution is the point Billentis draws out: the benefits of image-based PDFs sit mainly with the supplier, which is why larger recipients stay sceptical of them. Analysis from Politecnico di Milano, also cited in the report, put net benefits at 4–12 euros per invoice for VAT-compliant e-invoicing, rising to as much as 65 euros per cycle where the whole trade process is integrated.

These are 2017 figures; read them as a ratio, not a price list. The ratio is the argument. It is the same one behind Billentis’s estimate of a minimum 40 billion euro annual saving potential in Europe’s public sector, of which under 10% was then being exploited — an estimate whose model assumed 40% of e-invoices were unstructured PDFs and 60% structured XML, and which noted that administrations insisting on structured data only would do better.

What changes on 1 July 2030

ViDA — Council Directive (EU) 2025/516, adopted 11 March 2025 and in force since 14 April 2025 — resolves the contradiction by deleting one side of it. From 1 July 2030, Article 217 is replaced: an electronic invoice will mean one that, “at least in relation to the data referred to in Articles 262 and 271b”, has been issued, transmitted and received in a structured electronic format allowing automated processing. Recital 9 says plainly that this is being done to align the VAT definition with the one in Directive 2014/55/EU.

Four details matter more than the headline:

  • Hybrid invoices survive. Recital 9 explicitly covers invoices that combine a structured part with an unstructured human-readable part, provided all reportable data sits in the structured part. ZUGFeRD and Factur-X are not casualties. PDF-only is.
  • EN 16931 becomes the default, not the ceiling. The new Article 218(3) requires e-invoices to comply with the European standard, while letting member states allow other standards for domestic supplies outside the cross-border reporting scope.
  • Consent disappears. Under the revised Article 232, issuing an EN 16931-compliant e-invoice to a taxable person will not require the recipient’s acceptance.
  • The stakes rise from inconvenience to deductibility. ViDA lets member states provide that a customer may deduct or reclaim VAT only if it holds an e-invoice issued in the required format. At that point “legal but useless” stops being the failure mode; “not deductible” replaces it.

Two dates qualify the 2030 headline. Since 14 April 2025, member states no longer need a Commission derogation to mandate domestic e-invoicing — which is why the national mandates are arriving early. And member states that already had a domestic real-time transaction reporting obligation in place on 1 January 2024 have until 1 January 2035 to align those domestic systems.

Germany and Greece already flipped the definition

Germany is the cleanest illustration, because it changed the definition itself rather than bolting a reporting platform on top of the old one. Under the Wachstumschancengesetz, § 14 UStG redefined the electronic invoice with effect from 1 January 2025: a PDF sent by email is no longer an E-Rechnung but a sonstige Rechnung — an “other invoice”. The receiving obligation carried no transition period at all; every domestic business has had to be able to receive EN 16931-compliant invoices since 1 January 2025, and per the Federal Ministry of Finance’s guidance an email inbox is technically sufficient. Issuance is phased: paper and other electronic formats (with recipient consent) run through 2026, only businesses under 800,000 euros in prior-year turnover keep them in 2027, and from 1 January 2028 all domestic B2B invoices must be structured. In a hybrid invoice, the BMF’s October 2025 letter makes the structured part authoritative — and if the PDF layer disagrees with the XML, the divergent PDF can be treated as an additional invoice, with § 14c VAT liability attached.

Greece shows the same shift arriving through the tax-reporting door rather than the VAT-definition door. Authorised by Council Implementing Decision (EU) 2025/502, mandatory B2B e-invoicing went live on 2 March 2026 for businesses with over 1 million euros of 2023 revenue (penalties from 3 May 2026), with all remaining established businesses following on 1 October 2026. Invoices clear through myDATA, which returns a MARK and QR code — and an invoice never transmitted through the platform is not deductible for the buyer, regardless of whether the underlying transaction was real.

The pull-through effect was visible in Greece before either mandate. SAP’s August 2024 implementation guide for Greek e-invoicing records that once a company was issuing B2G invoices through a certified provider, the tax authority’s e-books rules forced it to submit all wholesale invoices — B2B included — through that same provider. The B2G requirement reached into B2B years ahead of the B2B mandate.

Set that against the 2016 compendium, where the Greek answer was the same as everyone else’s: no format required, PDF is fine. That answer was correct when it was written. It had an expiry date nobody printed on it.

Four things people get wrong

“PDFs are being banned”

No. Hybrid formats that embed structured data in a PDF container remain valid under ViDA, and member states can still permit other formats for transactions outside the reporting scope. What is ending is the PDF that contains nothing a machine can extract.

“It’s electronic, so it’s an e-invoice”

Only under Article 217 as it reads until 30 June 2030, and only where no national mandate says otherwise. In Germany that sentence has been wrong since January 2025.

“The B2G directive forces suppliers to send structured invoices”

It forces authorities to receive them. Your obligation to send comes from national law, which varies by country.

“An e-invoice is an e-invoice for both parties”

Not necessarily. Under the French rules recorded in the 2016 compendium, a recipient who printed an electronic invoice and deleted the data file was no longer holding an electronic invoice at all — on their side. Status can depend on what the receiver does after delivery, which is also why archiving the structured original matters: France requires the original format for three years, and Germany requires at least the structured part of an E-Rechnung to be kept intact.

Frequently asked questions

Is a PDF invoice legal in the EU?

Yes, for VAT purposes, under the current Article 217 definition — provided you can ensure authenticity of origin, integrity of content and legibility, typically through business controls with a reliable audit trail. That changes where a national mandate has already redefined the term, as in Germany since January 2025 and Greece for in-scope businesses since March 2026.

Does a PDF invoice need a digital signature?

Generally no. In the 22 countries surveyed in the 2016 PSP compendium, almost all answered that no digital signature was required where authenticity and integrity were otherwise ensured; Hungary (signature or EDI) and Romania (extended signature on a qualified certificate) were the exceptions of the time. Signatures are one permitted method under Article 233, not a requirement.

Is ZUGFeRD or Factur-X a PDF or an e-invoice?

Both, and that is the point. They are hybrid formats: a human-readable PDF carrying structured XML. ViDA’s recital 9 confirms hybrids fall inside the new definition as long as all reportable data is in the structured part. In Germany, the structured part governs if the two layers disagree.

Do I still need the buyer’s consent to send an e-invoice?

Today, yes in most cases — Article 232 makes electronic invoicing subject to recipient acceptance, though the 2016 compendium found that acceptance could usually be given tacitly, in Hungary even by simply paying the invoice. From 1 July 2030 consent falls away for EN 16931-compliant invoices issued to taxable persons, and member states have been able to remove it domestically since April 2025.

How long do I have to keep an electronic invoice?

There is no single EU answer. Periods in the 2016 compendium ran from five years to eleven, with longer terms for real estate and investment goods. Check the rule in each country where you are established or registered, and check the format condition as well as the duration.

Posted by admin in EU E-Invoicing & Tax Reporting Knowledge Base